InfoHawk finds 820 fake restaurant sites, some skimming card data
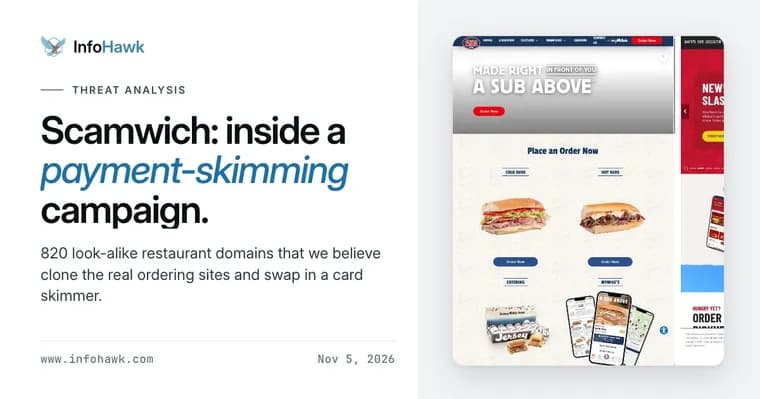
InfoHawk, a research group, has published a report called "Scamwich" describing a network of 820 suspicious domains that impersonate major US restaurant chains. The brands named include Jersey Mike's, Jimmy John's, Firehouse Subs, Chipotle and Dave's Hot Chicken. According to InfoHawk, some of the sites run payment-skimming attacks that capture credit card information and ask customers for their bank's SMS verification codes.
The researchers say they investigated the sites in early November 2026 and that the domains appear to be part of one or more coordinated restaurant impersonation and payment-skimming operations. Across two research passes they identified 820 domains impersonating 35 restaurant brands. Of those, 808 use the .delivery top-level domain; the rest use .com or .shop. Most are typosquats, with a few look-alike .com and .shop names. The report's brand table lists the date range for each brand's domains, all in 2026.
The investigation began with one domain, mlckessejersstey[.]delivery, which impersonated Jersey Mike's and reproduced its online ordering experience. InfoHawk says the attackers did not build a crude imitation. Instead they reverse-proxied the legitimate site while replacing the checkout payment form with a malicious one. A reverse proxy fetches content from a legitimate website and shows it to visitors under a different domain, so the attacker's site can display genuine pages and assets while changing only the parts that matter to the attacker.
The malicious checkout asked for credit card details and also for the SMS verification code sent by the customer's bank. InfoHawk calls this a particularly dangerous combination: a card number is valuable to criminals, and a one-time code could also help them authorize fraudulent transactions, depending on how the victim's bank uses that code.
For customers, the report says, the experience can look nearly identical to ordering from the restaurant. The site looks familiar, the menu and ordering flow can behave normally, and the fraudulent payment form appears at exactly the moment a customer expects to pay. The attack does not require the restaurant's own website to have been hacked: the attackers run their own infrastructure and use the authentic site as the source of the content they display.
The brand table shows Jimmy John's as the most heavily cloned brand, with 404 domains seen between Mar 3 and Oct 21, 2026. The report lists them (the text available here breaks off partway through the list), and they are misspellings of the brand name and "sandwich" such as jimmijones[.]delivery and jimmysandwich[.]delivery. Counts for the other 34 brands are not in the portion of the report available here.
Key facts
- InfoHawk identified 820 domains impersonating 35 US restaurant brands across two research passes; 808 use the .delivery top-level domain and the rest use .com or .shop.
- Impersonated brands include Jersey Mike's, Jimmy John's, Firehouse Subs, Chipotle and Dave's Hot Chicken; Jimmy John's alone accounts for 404 of the domains.
- On the site that started the investigation (mlckessejersstey[.]delivery), attackers reverse-proxied the real Jersey Mike's site and replaced the checkout form with a malicious one.
- The fake checkout asked for card details and the bank's SMS verification code; InfoHawk says only some of the sites run these skimming attacks.
- The attack does not require the legitimate restaurant's website to have been hacked.
Why it matters
The scale is large: 820 domains across 35 brands, built to look like ordinary food ordering. What sets the campaign apart, in InfoHawk's account, is the method. Because the attackers reverse-proxy the real site, the menu and ordering flow can behave normally, and only the payment form at the moment of paying is fake. Asking for the bank's SMS code as well as the card number adds a second piece of data that, depending on the bank, could help authorize fraudulent transactions.
Who it affects
Customers who order online from the impersonated chains are the direct targets: the report names Jersey Mike's, Jimmy John's, Firehouse Subs, Chipotle and Dave's Hot Chicken among 35 brands. The restaurants are affected as brands being imitated, though InfoHawk says their own websites do not need to be compromised for the attack to work. Banks are involved indirectly, since the stolen SMS codes are meant to be their verification step.
How to use it
This is a threat-research report, not a product. Its practical value is the indicators: the brand table lists the cloned domains per brand, and the Jimmy John's list is only partly visible in the text reviewed here, which is cut off mid-list. Security teams can compare these against their own logs or blocklists. The domains are typosquats, such as mlckessejersstey[.]delivery for Jersey Mike's, so the address is where the imitation shows even when the page itself looks right.
How solid is it
The report comes from InfoHawk, a security research group, and is a detailed write-up with a brand table and domain lists. The figures (820 domains, 35 brands, 808 on .delivery, 404 for Jimmy John's) are InfoHawk's own counts. Its findings are stated with some care: the sites "appear to be" part of one or more coordinated operations, and only "some" run the skimming attacks. The text available here is cut off partway through the domain lists, so the rest of the report is not covered.
Risks and caveats
The report does not say how many of the 820 domains actually run the skimming checkout, only that some do. The text reviewed here does not say how many victims there are or how much money was stolen, who runs the operation, how people reach the fake sites, or whether any chain has responded or any domains have been taken down. The note about SMS codes is hedged by InfoHawk itself: a code could help authorize fraud, depending on how the victim's bank uses it. Per-brand counts beyond Jimmy John's are not available in the reviewed text.
“Importantly, this does not require the legitimate restaurant's website to have been hacked.”
— InfoHawk, Scamwich report